As AI becomes more capable and increasingly autonomous, it also becomes a new attack surface. What happens when an AI System / Solution is manipulated, impersonated, poisoned, stolen, compromised or simply goes wrong?
Financial Technology Frontiers (FTF)’s 10-part AI Security Risks Series examines the ten key AI Security Risks highlighted by the Canadian Centre for Cyber Security (CCCS), and goes beyond technology to explore the What, How, Impact and Control of each Risk. This series is designed to give Business Leaders and Technology, Cybersecurity, Risk and Compliance Professionals a practical framework for understanding and managing the many faces of AI Risk.
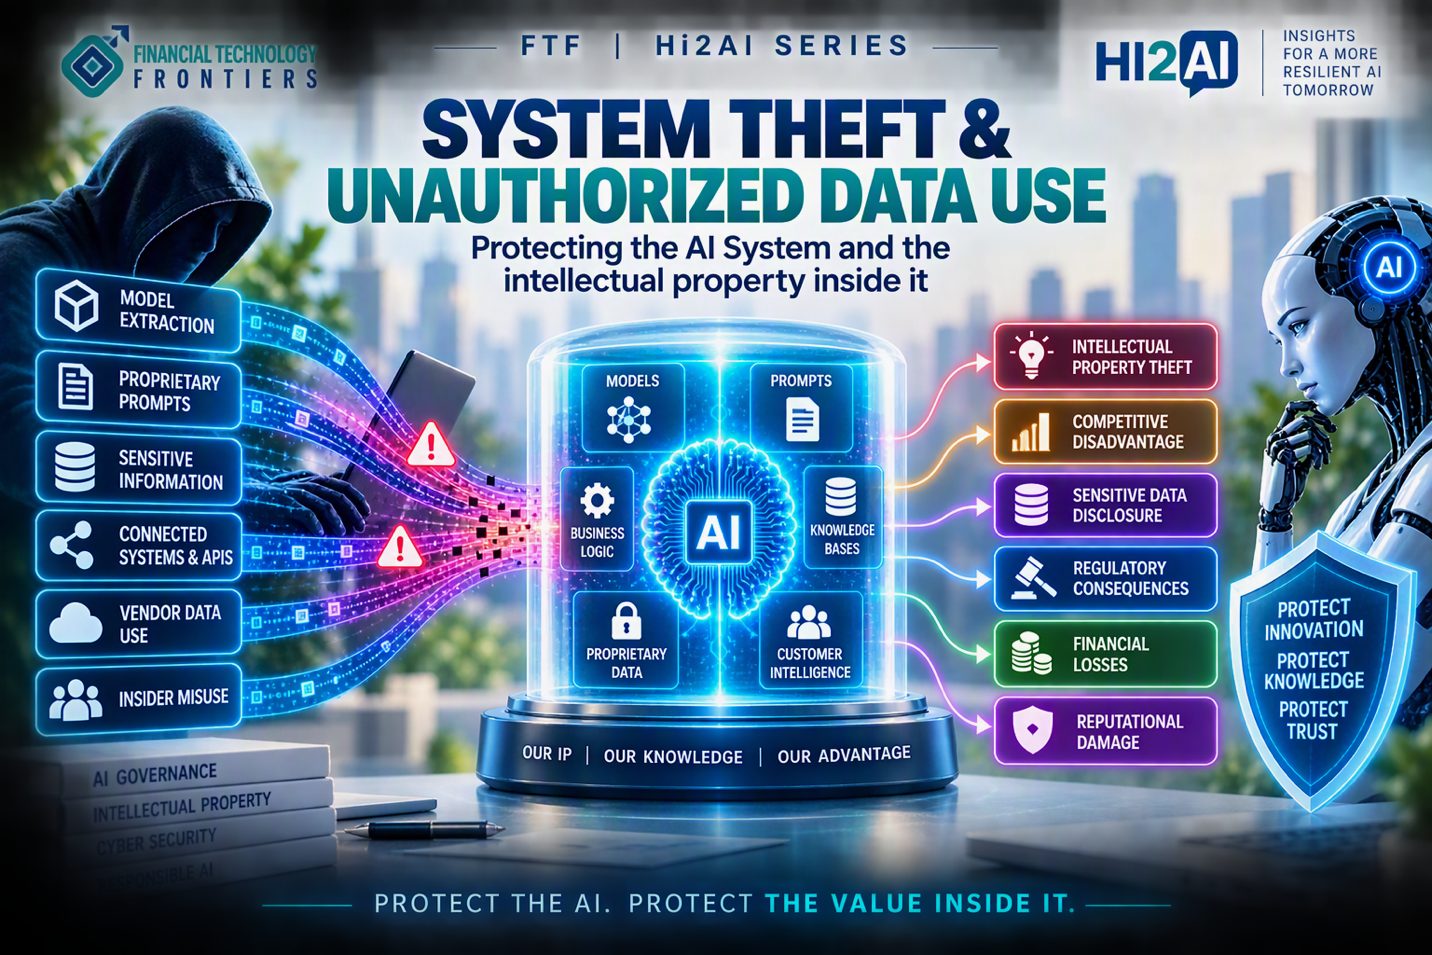
AI Systems can represent substantial investments in intellectual property, proprietary knowledge, business processes and competitive advantage. Many Organizations focus on the outputs generated by AI. However, the AI System itself may be one of the Organization’s most valuable assets. AI Models, Agents, Prompts, Decision Logic, Knowledge Bases and Connected Data Sources can collectively contain years of accumulated expertise, operational knowledge and Intellectual Property.
As AI adoption grows, attackers may increasingly seek not only to manipulate AI Systems, but also to copy them, extract sensitive information from them or exploit them to gain access to valuable organizational Data.
What Is It All About?
System Theft and Unauthorized Data Use occur when attackers, competitors, malicious insiders or even trusted third parties gain unauthorized access to an AI System, its underlying components or the information it contains.
One form of attack involves attempting to reproduce, clone or copy a proprietary AI System by repeatedly interacting with it and analysing its outputs. Another form of attack involves extracting sensitive information, proprietary knowledge or confidential Data that may be accessible through the AI System.
Organizations must carefully consider how AI System vendors and Service Providers collect, retain, process and potentially use information submitted on their Platforms. In some cases, Data shared with an AI System may subsequently be used to improve Models, support Model training activities or be retained for longer periods than intended or agreed.
As AI becomes increasingly embedded within business operations, protecting both the AI System and the information it contains becomes a critical concern not only for Security, but also for Governance and Intellectual Property protection.
How Does This Threat Attack?
Attackers may attempt to extract value from an AI System without necessarily compromising it in a conventional sense. The objective may be to replicate the System, understand its internal logic, obtain proprietary information or gain access to sensitive Data. Attack techniques may include:
- ■Model Extraction and AI System ReplicationAttackers may repeatedly query an AI System and analyse its responses to understand how it behaves. By collecting sufficient inputs and outputs, they may construct a substitute Model that approximates the behaviour of the original AI System. Over time, this can allow competitors or threat actors to replicate valuable AI capabilities without incurring the cost of developing them independently.
- ■Extraction of Proprietary Prompts and Decision LogicAI Systems often rely upon engineered Prompts, Instructions, Rules and Decision Frameworks that reflect significant organizational expertise. Attackers may attempt to manipulate the AI System into revealing this information, enabling them to reproduce proprietary workflows, methodologies or business processes.
- ■Disclosure of Sensitive or Confidential InformationAI Systems may have access to Customer Data, Internal Documents, Financial Information, Intellectual Property and other sensitive content. Attackers may attempt to exploit weaknesses in the AI System to retrieve information that should not be accessible, thus potentially exposing valuable organizational assets.
- ■Abuse of Connected Tools, Data Sources and IntegrationsModern AI Systems increasingly connect to Databases, Applications, APIs and Enterprise Platforms. Attackers may exploit these connections to access information beyond what they are authorized to view or use, expanding the impact beyond the AI System itself.
- ■Unauthorized Vendor Data UseOrganizations frequently interact with Third-Party AI Providers and Cloud-Based AI Services. If contractual safeguards and technical controls are insufficient, sensitive information submitted to these services may be retained, processed or used in ways that exceed the Organization’s expectations or intended use.
- ■Insider Misuse and Unauthorized AccessEmployees, Contractors or other authorized users may intentionally or unintentionally expose AI Models, Training Assets, Prompts or sensitive organizational information. Because insiders often possess legitimate access, these risks can be particularly difficult to detect and manage.
The attackers’ objective may not be to disrupt the AI System. Instead, attackers may seek to quietly extract value from it while allowing normal operations to continue uninterrupted.
What Harm Can This Risk Do?
The consequences of System Theft and Unauthorized Data Use can extend far beyond the loss of a single AI Application. Potential impacts include, but are not limited to:
- ■Intellectual Property TheftAI Models, Prompts, Agents, Knowledge Assets and Decision Frameworks often represent significant investments of time, expertise and capital. Unauthorized access or replication can result in the loss of valuable Intellectual Property that differentiates the Organization from its competitors.
- ■Competitive DisadvantageIf attackers or competitors can reproduce key AI capabilities, the Organization may lose part of the competitive advantage it has developed through innovation, investment and operational experience. Years of accumulated expertise may become available to others at a fraction of the original cost and time.
- ■Loss of Proprietary Business KnowledgeMany AI Systems embed organizational processes, decision-making methodologies, pricing strategies, operational procedures and industry expertise. Disclosure of this information may reveal how the Organization operates and make core business capabilities easier to replicate.
- ■Sensitive Information DisclosureUnauthorized access to Customer Information, Employee Information, Financial Data, Product Plans or Strategic Documents may expose the Organization to Security, Privacy and Regulatory risks. In some cases, the disclosure itself may be more damaging than the theft of the AI System.
- ■Increased AI Development and Security CostsOrganizations affected by AI System theft may need to redesign Models, rebuild Knowledge Assets, strengthen Security Controls, conduct investigations and implement additional monitoring capabilities. These activities can create significant financial and operational burdens.
- ■Regulatory and Compliance ConsequencesUnauthorized exposure of personal, confidential or regulated information may create legal, contractual and regulatory obligations. Organizations may be required to conduct notifications, investigations and remediation activities depending on the nature of the information involved.
- ■Reputational Damage and Loss of Stakeholder TrustCustomers, Investors, Business Partners and Regulators expect Organizations to protect both sensitive information and valuable Intellectual Property. A failure to safeguard AI Systems and their associated knowledge assets can damage confidence in the Organization’s ability to manage AI responsibly.
The challenge is that Organizations may not immediately recognize that valuable information is being extracted. In many cases, the AI System continues to operate normally while proprietary knowledge, competitive advantages or sensitive information are quietly being copied, collected or exposed.
What Can Organizations Do To Control This Risk?
Protecting AI Systems requires more than traditional Cybersecurity Controls. Organizations must recognize that AI Systems increasingly represent repositories of valuable intellectual property, decision-making logic and sensitive information. Controls should therefore focus on protecting both the AI System and the assets contained within it. Organizations should:
- ■Establish Strong Access Controls and AuthenticationOrganizations should ensure that access to AI Systems, Models, APIs and Knowledge Assets is granted only to authorized users and services following strict Identity Guidelines. Other controls including strong Authentication, Least Privilege Principles and Segregation of Duties should be leveraged to help reduce the risk of unauthorized access and misuse.
- ■Monitor for Model Extraction and Abnormal Query ActivityOrganizations should continuously monitor API Usage Patterns, Query Volumes and User Behaviour to identify attempts to harvest outputs or replicate AI capabilities. Rate Limiting, Behavioural Analytics and Automated Alerting can help detect suspicious activity before significant extraction occurs.
- ■Protect Sensitive Information and Intellectual PropertyPrompts, Model Configurations, Knowledge Bases, Business Rules and Sensitive Data should be treated as high-value assets. Data Loss Prevention, Encryption and Information Classification processes can help reduce the risk of unauthorized disclosure.
- ■Govern Vendor Data Use and Retention PracticesOrganizations should establish clear contractual requirements governing how AI Vendors may store, retain, process or use organizational information. Appropriate controls should be included in contracts, such as “No Training of AI Models”, “Mandatory Disclosures and Reporting” where necessary, limitations on Data Retention and regular assessments of Vendor practices.
- ■Secure Connected Systems and Enterprise IntegrationsAI Systems connected to Databases, Applications, APIs and Enterprise Platforms should be subject to strong Security Controls and continuous monitoring. Organizations should ensure that AI Systems operate only within authorized permissions and approved usage boundaries.
- ■Regularly Assess AI Security and Intellectual Property RisksOrganizations should incorporate AI-specific risks into Security Reviews, Risk Assessments, Vendor Evaluations and Red Team Exercises. Periodic testing helps identify weaknesses before they lead to the loss of valuable information or proprietary AI capabilities.
Organizations should recognize that protecting AI Systems is not solely a Cybersecurity challenge. It is also an Intellectual Property, Data Governance, Vendor Risk Management and Business Resilience concern.
FTF Analysis
System Theft and Unauthorized Data Use highlight a significant shift in how Organizations should think about AI Security. Traditionally, Security programs focused on protecting IT Systems from disruption, unauthorized access or operational compromise. In the AI era, Organizations must also protect the knowledge, intelligence and competitive advantages embedded within those AI Systems.
The asset at risk is not always the AI Model itself. In many cases, far greater value resides in the proprietary Prompts, Business Rules, Decision Logic, Knowledge Repositories, Customer Intelligence, Operational Processes and Training Assets that surround the Model. The critical question therefore becomes:
“If an attacker gained access to this AI System, what valuable knowledge, capability or competitive advantage could they take with them?”
As AI Systems become increasingly integrated with Enterprise Data, Applications and Business Processes, the distinction between protecting Data, protecting Intellectual Property and protecting AI Systems will continue to blur.
FTF believes Organizations should increasingly view AI Security as an extension of Intellectual Property Protection. The objective is not simply to prevent unauthorized access to an AI System. It is to protect the unique organizational knowledge, expertise and competitive advantages that the AI System represents.
The future challenge will not only be building capable AI Systems. It will be protecting the value that those AI Systems contain.
About This Article
This Article examines System Theft and Unauthorized Data Use as emerging AI Security risks that affect Organizations who increasingly seem to rely on AI Systems, Agents and AI-enabled Business Processes. The Article explores how attackers may seek to replicate AI capabilities, extract proprietary knowledge or gain access to sensitive information, and considers Governance, Security and Intellectual Property Controls that Organizations should establish to protect AI Systems and the valuable assets they contain.
This Article is authored by Narasimham Nittala who leads the Strategy and Research vertical of Financial Technology Frontiers (FTF). This Article is published as part of FTF’s Hi2AI Series. Like our previously published Articles, this Article is written in an accessible, practitioner-focused format and it aims to raise awareness about responsible AI adoption across various Institutions.
FTF believes that service providers, Fintech entities, consulting firms and technology companies can all benefit from reflecting on the perspectives shared here and consider how their own approaches to AI Risk Management can evolve. Practitioners in various industries are equally encouraged to adapt these insights to their unique contexts.
About Hi2AI
Hi2AI is FTF’s AI ecosystem for Financial Services. Hi2AI is a trusted community shaping the future of Artificial Intelligence in Financial Services by driving responsible innovation, influencing policy with regulators, and crafting future standards that ensure growth, resilience, and trust across the global financial ecosystem. Hi2AI exists to accelerate the responsible adoption of AI across the global financial ecosystem through:
- AI-Driven Industry Collaboration
- Ecosystem Connection & Innovation
About Financial Technology Frontiers
Financial Technology Frontiers (FTF) is a global media-led fintech platform dedicated to building and nurturing innovation ecosystems. We bring together thought leaders, financial institutions, fintech disruptors, and technology pioneers to drive meaningful change in the financial services industry.